Armor Wallet
Crypto, DeFi, Web3 infrastructure
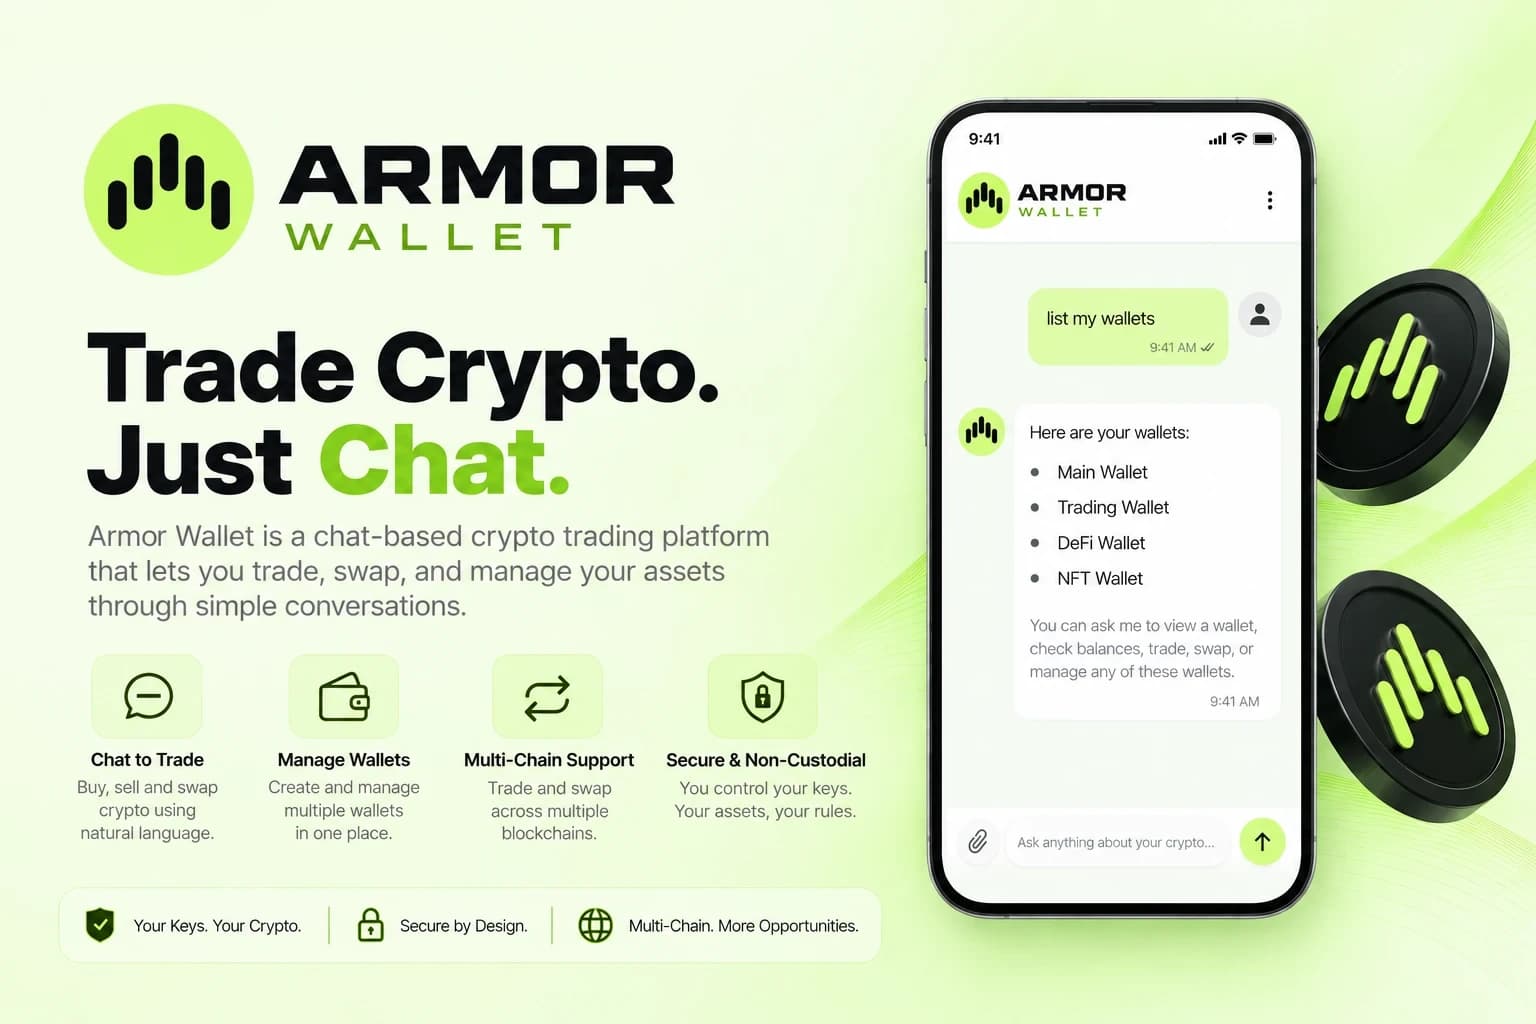
An open-source MCP server and agent layer that lets AI assistants carry out real crypto operations: wallet management, swaps, DCA and limit orders, and staking.
AI agents that investigate network incidents like a senior NOC engineer: parallel checks on real devices, correlated evidence with a confidence score, and a scoped fix for an engineer to approve.
Network incidents are slow to diagnose because the evidence is scattered across vendor devices, operating systems, telemetry, logs and configs. On-call engineers log into box after box to piece the story together, often in the middle of the night.
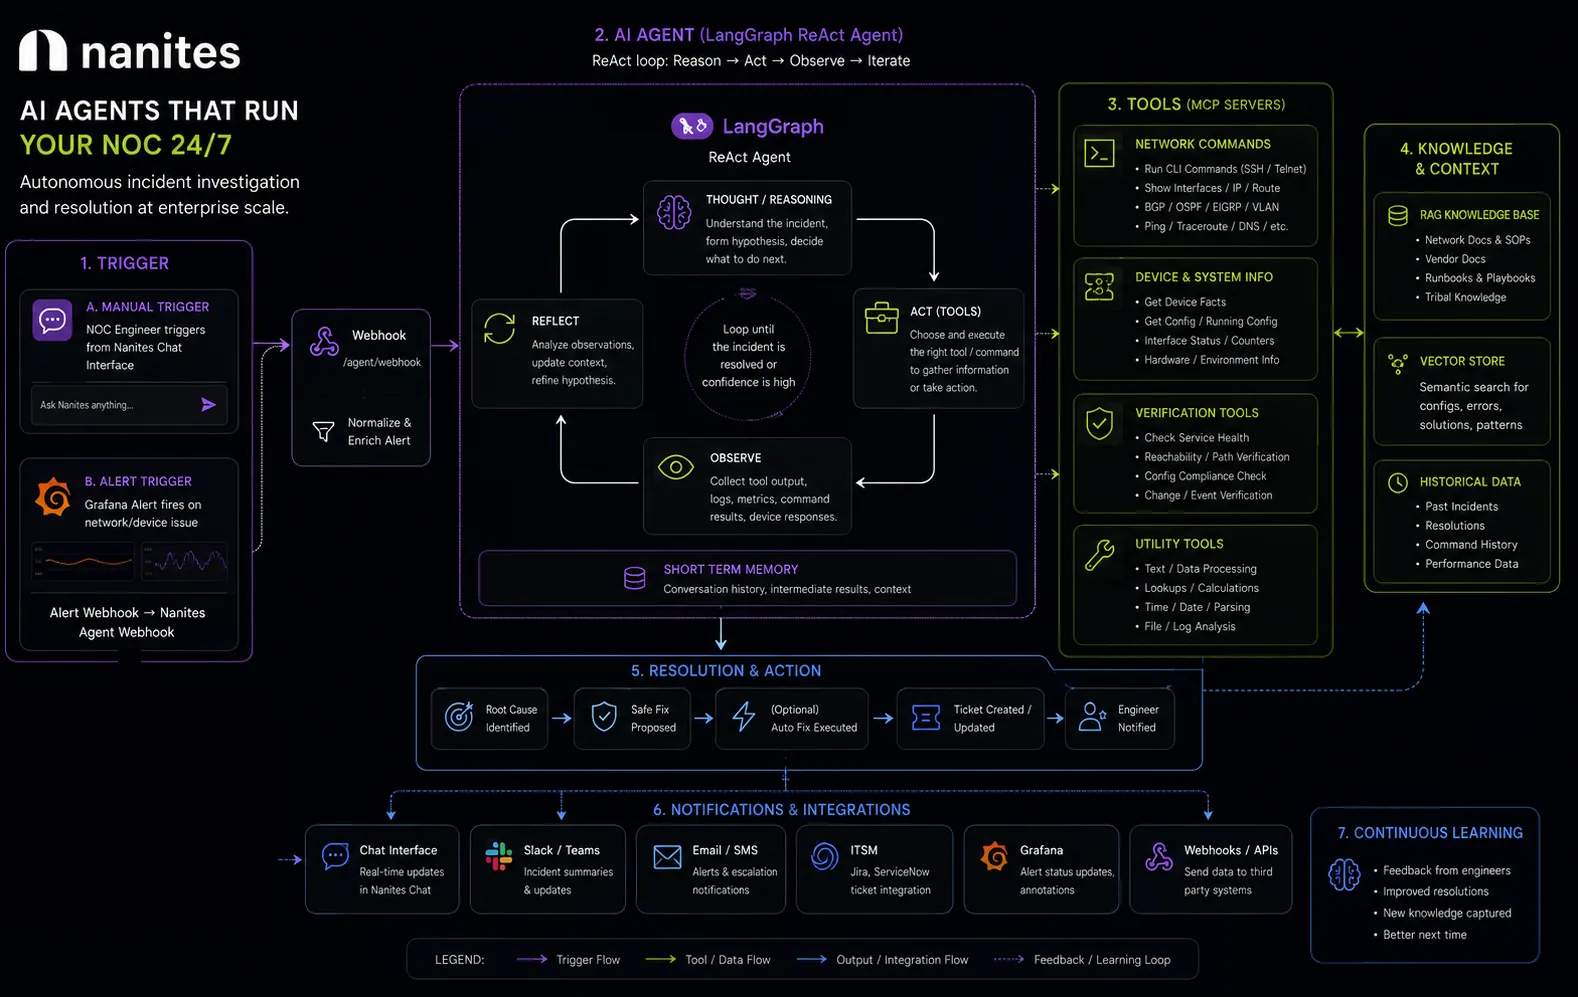
Built a ReAct-style investigation agent with LangGraph and LangChain. A Grafana alert triggers it, and it sets a goal and pulls the relevant context.
Spawns a sub-agent for each device, which connects and runs real read-only commands, so checks across devices happen in parallel.
Normalises vendor differences before comparing, for example IOS-XR layer-2 MTU against IP MTU, so a flagged mismatch is real rather than a reporting artefact.
Correlates the findings into an evidence list with a confidence score, then proposes a scoped fix for an engineer to review and apply.
Engineers can ask follow-up questions against the same investigation context.
Built evaluation sets from recorded incidents and device outputs, including synthetic failure scenarios run on a network testbed.
Evaluated the agent's reasoning and root-cause findings after every iteration, locally and against the testbed.
Traced every run in LangSmith, from the incoming alert to the proposed fix.
Alert-triggered investigation agent
Per-device sub-agents for parallel checks
Vendor and OS normalisation logic
Evidence and confidence reporting
Follow-up questions on an investigation
LangSmith tracing
Crypto, DeFi, Web3 infrastructure
An open-source MCP server and agent layer that lets AI assistants carry out real crypto operations: wallet management, swaps, DCA and limit orders, and staking.
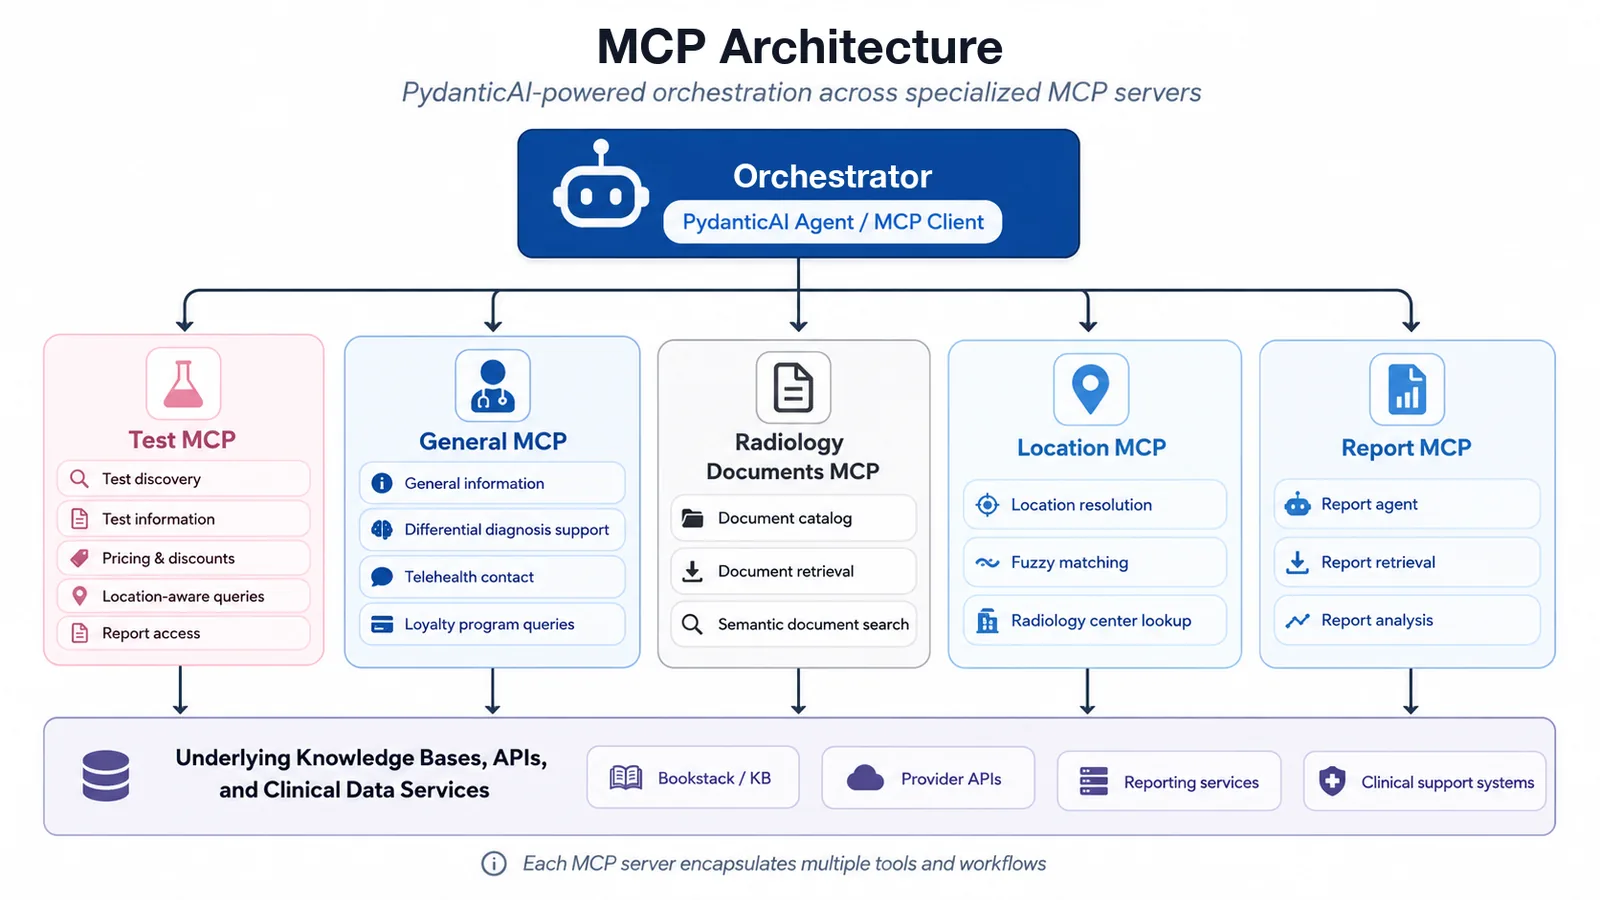
Healthcare, Diagnostics
An AI agent layer for a diagnostics network whose patient app has 1M+ downloads: plain-language lab-report explanations, test guidance, lab lookup and voice, orchestrated across MCP tool servers.
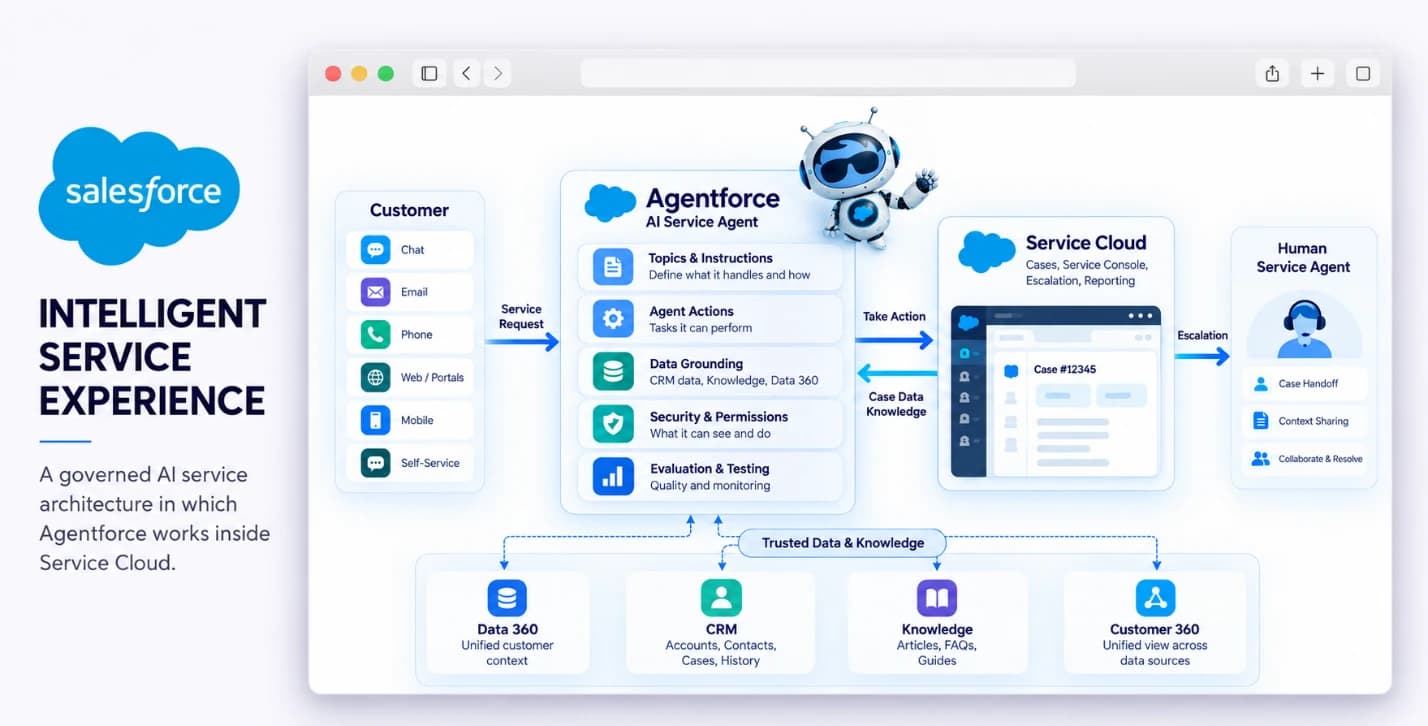
Enterprise customer service
A governed AI service architecture in which Agentforce works inside Service Cloud. It is grounded in Data 360 context and Knowledge, scoped by topics and instructions, and always able to hand off to a human agent.
We can scope and build a system with comparable capabilities, shaped around your own workflows, data and integrations.